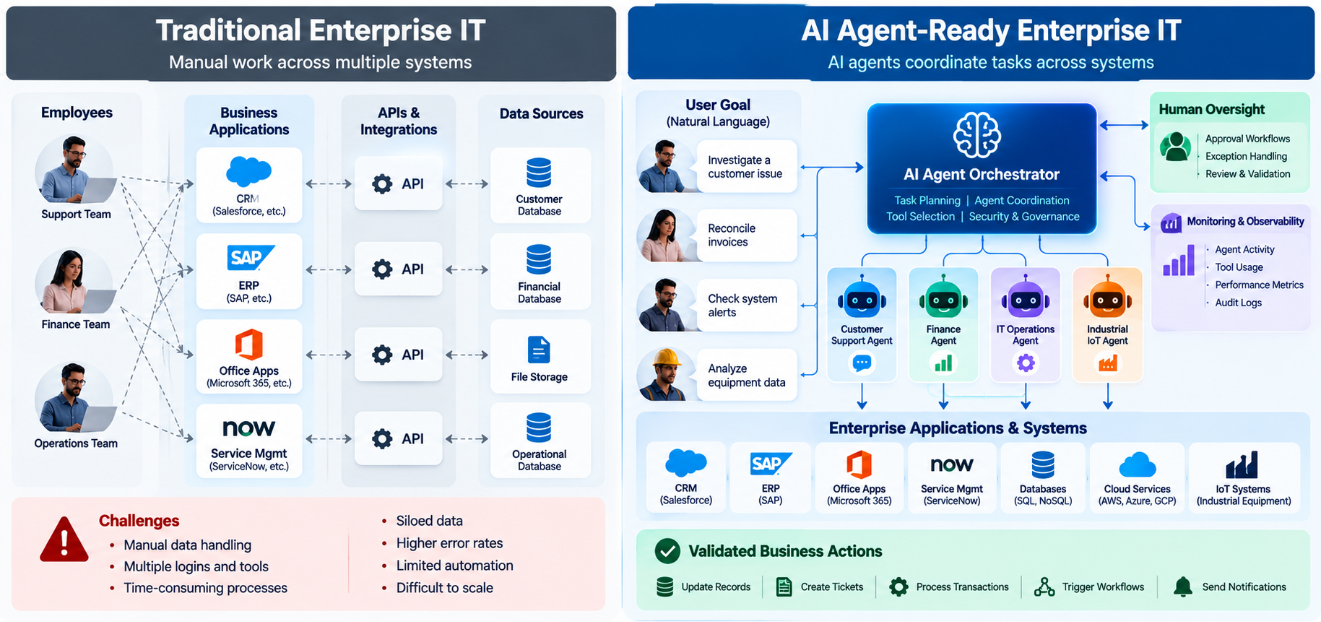

AI Agents Are Becoming Digital Employees. Is Your IT Architecture Ready?

Enterprise AI is entering a new phase. Instead of simply answering questions, AI systems are beginning to execute tasks, coordinate workflows, access business applications, and make decisions within defined boundaries.
An AI agent might investigate a customer complaint, retrieve information from multiple systems, update a service ticket, and recommend the next action without requiring someone to manage every step.
However, giving AI agents access to enterprise systems introduces new architectural challenges.
Traditional IT infrastructure was designed primarily around human users, applications, and predefined integrations. AI agents introduce software entities that can independently select tools and initiate actions.
This article explores how AI Agent Architecture for Enterprises can support these digital workers while maintaining security, reliability, visibility, and human control.
What Is AI Agent Architecture for Enterprises?
AI Agent Architecture for Enterprises is the technical framework that allows autonomous or semi-autonomous AI agents to interact with enterprise applications, data sources, APIs, and business workflows securely.
Unlike traditional automation, where developers explicitly define each step, AI agents can interpret goals, select available tools, and determine which actions to perform.
Consider a customer support operation.
A traditional chatbot might answer a customer's question about an order.
An AI agent could go further by checking the order management system, retrieving shipping information, reviewing relevant policies, creating a support ticket, and preparing a refund request.
The difference is not simply better language understanding.
It is the ability to move from generating information to executing controlled business actions.
Why Enterprise Architecture Must Change
Most enterprise systems follow relatively predictable interaction patterns.
A user logs into an application, performs an authorized action, and receives a result.
An AI agent introduces a different workflow.
The agent receives a goal, determines which systems are relevant, selects tools, processes information, and may initiate multiple actions before returning a result.
This creates several architectural requirements.
Identity management: Every agent needs an identifiable identity, just as employees and applications do.
Access control: Agents must access only the systems and operations necessary for their assigned responsibilities.
Workflow orchestration: Organizations need mechanisms to coordinate tasks across agents, applications, and human employees.
Observability: IT teams must understand what an agent attempted, which tools it used, and whether the outcome was successful.
Governance: Sensitive or irreversible actions must follow organizational policies and approval procedures.
Reliability: Agents must handle incomplete information, application failures, and unexpected responses without causing uncontrolled downstream actions.
These requirements make agentic AI architecture an enterprise infrastructure concern rather than simply an AI model selection exercise.
Why AI Agents Are Being Compared to Digital Employees
The comparison is useful because AI agents can be assigned responsibilities within business processes.
A digital support agent may investigate incidents.
A digital finance agent may reconcile transactions.
A digital operations agent may monitor equipment performance.
A digital procurement agent may compare supplier quotations.
However, AI agents are not employees in the legal or organizational sense. They do not possess independent accountability, and their actions remain the responsibility of the organization deploying them.
The comparison is most valuable when designing operational controls.
If a human employee requires permissions, supervision, performance monitoring, and escalation procedures, an AI agent performing similar tasks needs equivalent technical safeguards.
Benefits and Trade-Offs
Enterprise AI agents can potentially reduce repetitive work, improve response times, and connect processes that currently require manual coordination.
They may also allow employees to focus on exceptions and decisions that require judgment.
However, these benefits depend on workflow design.
An agent that saves five minutes on data retrieval but introduces frequent errors requiring manual correction may provide little operational value.
Similarly, an agent with broad system permissions might execute tasks efficiently while introducing unacceptable security risks.
The objective should therefore be controlled operational improvement, not maximum autonomy.
How Enterprise AI Agent Architecture Works
A practical enterprise AI agent architecture contains several interconnected layers.
Each layer addresses a specific responsibility, from understanding a request to executing actions and recording outcomes.
1. User and Business Application Layer
This is where an AI agent receives instructions.
Requests may originate from employees, customers, enterprise applications, scheduled workflows, or connected devices.
For example, a maintenance supervisor might request:
"Investigate why Machine 12 has generated repeated temperature alerts."
The request becomes the starting point for an agent-driven workflow.
2. AI Agent Orchestration Layer
The orchestration layer manages how tasks are assigned and executed.
It may coordinate a single agent or multiple specialized agents.
For example, an industrial maintenance workflow could involve:
- A monitoring agent that examines sensor data.
- A diagnostic agent that investigates abnormal readings.
- A maintenance agent that reviews service history.
- An inventory agent that checks spare-part availability.
- A scheduling agent that proposes a maintenance window.
The orchestration layer manages task dependencies, execution status, retries, and escalation.
It should also prevent duplicate or conflicting actions.
3. AI Reasoning and Model Layer
This layer provides the language understanding and reasoning capabilities used by agents.
Large language models can interpret instructions, analyze retrieved information, and select appropriate tools.
However, not every operation requires a powerful model.
Simple classification, formatting, and routing tasks may be handled by smaller models or conventional software rules.
More complex investigations may require stronger reasoning models.
A well-designed architecture routes tasks according to complexity, sensitivity, latency, and cost.
This avoids using expensive AI inference for operations that deterministic software can perform more reliably.
4. Tool and Integration Layer
AI agents become operationally useful when they can interact with enterprise systems.
Common integrations include:
- Customer relationship management platforms.
- Enterprise resource planning systems.
- Service management applications.
- Cloud infrastructure.
- Databases and analytics platforms.
- Document management systems.
- Industrial IoT platforms.
- Internal APIs.
The integration layer exposes approved operations through controlled interfaces.
For example, a support agent might receive permission to read customer records and create support tickets but not delete accounts or approve refunds.
This separation limits the consequences of incorrect decisions.
5. Enterprise Data and Knowledge Layer
Agents require reliable information to perform useful work.
Enterprise knowledge may exist across structured databases, internal documentation, knowledge bases, and operational systems.
Retrieval-augmented generation, commonly called RAG, allows an AI system to retrieve relevant information before producing a response.
For example, a diagnostic agent may retrieve equipment manuals, maintenance records, and historical sensor readings.
However, retrieved information must be treated as data rather than trusted instructions.
A malicious or inaccurate document should not be allowed to override the agent's operating rules.
6. Security and Governance Layer
Security controls should apply throughout the architecture.
Important controls include agent identity, authentication, authorization, audit logging, policy enforcement, and approval workflows.
For sensitive actions, organizations should require explicit human approval.
Examples include financial transactions, production infrastructure changes, access-right modifications, and safety-critical equipment commands.
7. Monitoring and Observability Layer
Enterprise teams need visibility into agent behavior.
Monitoring should capture task execution, model usage, tool calls, errors, latency, cost, and approval events.
It should also connect agent activity to business outcomes.
For example, resolving a customer support ticket is more meaningful than simply counting successful model responses.
A Reference Enterprise AI Agent Architecture
A practical workflow can be represented as:
Employee or Application Request
↓
Enterprise AI Gateway
↓
Authentication and Policy Validation
↓
AI Agent Orchestrator
↓
AI Models and Specialized Agents
↓
Approved Tools and Enterprise APIs
↓
Business Applications, Databases, Cloud, and IoT Systems
↓
Result Validation and Human Approval Where Required
↓
Business Action and Audit Record
The security and monitoring layers operate across the entire workflow rather than appearing only at the beginning or end.
This architecture allows organizations to introduce AI agents without giving them unrestricted access to existing systems.
Need to evaluate how AI agents would fit into your existing applications, cloud infrastructure, or IoT platform? Infolitz Software can help assess integration requirements and identify practical architectural options.
Tools and Technology Stack Options for Enterprise AI Agents
Enterprise AI architecture does not depend on a single framework or model provider.
Organizations can combine several technologies based on their existing infrastructure, security requirements, and operational objectives.
AI Agent Development Frameworks
Agent development frameworks help developers implement tool usage, workflow coordination, state management, and model interactions.
Popular options include LangGraph, Microsoft AutoGen, and CrewAI.
LangGraph is useful when applications require explicit workflow state and controlled execution paths.
AutoGen supports patterns for building applications involving collaborating agents.
CrewAI provides abstractions for organizing agents around tasks and workflows.
The choice should depend on operational requirements rather than framework popularity.
For example, an enterprise workflow involving financial approvals may benefit from explicit state transitions and deterministic approval gates.
A research-oriented workflow may require more flexible agent collaboration.
Model Selection
Enterprise agents may use hosted frontier models, smaller cloud models, or locally deployed language models.
Hosted models can simplify initial deployment and provide access to advanced capabilities.
Locally deployed models may offer greater control over infrastructure and data processing, although they introduce additional maintenance responsibilities.
Organizations should evaluate model accuracy, latency, deployment restrictions, security requirements, and total operating costs.
Model choice should also reflect the consequences of failure.
A model that performs adequately for document categorization may not be appropriate for deciding whether an industrial system should be restarted.
Model Context Protocol
The Model Context Protocol (MCP) provides a standardized approach for connecting AI applications to external tools and information sources.
Without a common interface, developers may need to build custom integrations for every combination of agent and enterprise application.
MCP can simplify this integration challenge by defining common interaction patterns.
However, MCP does not automatically make integrations secure.
Organizations still need authentication, authorization, input validation, and restrictions on permitted operations.
Agent-to-Agent Communication
The Agent2Agent (A2A) Protocol addresses communication between independent agents.
For example, a customer support agent may delegate a billing investigation to a finance agent.
The finance agent can perform its assigned task and return a result.
A2A and MCP address different integration needs.
MCP primarily helps agents interact with tools and resources.
A2A helps independently implemented agents communicate and coordinate.
Both may be useful within a larger enterprise architecture, but neither is mandatory for every deployment.
Cloud and Infrastructure Options
Enterprise agents can operate on public cloud platforms, private infrastructure, or hybrid environments.
Cloud deployments may simplify scaling and managed-service integration.
Private deployments can provide greater infrastructure control.
Hybrid architectures allow organizations to keep sensitive workloads within controlled environments while using cloud services for selected tasks.
The appropriate approach depends on data residency, network connectivity, operational requirements, and compliance obligations.
Best Practices for Enterprise AI Agent Deployment
Successful AI agent deployment requires more than connecting a language model to business applications.
Organizations should establish clear operational boundaries before expanding autonomy.
Start With a Narrow Business Workflow
Choose a workflow with measurable outcomes and manageable risk.
Examples include classifying support tickets, summarizing incidents, retrieving maintenance documentation, or preparing operational reports.
Avoid beginning with processes that require unrestricted access to multiple critical systems.
Define Agent Responsibilities
Every agent should have a clear purpose.
Specify which tasks it can perform, which systems it can access, and which decisions require human intervention.
An agent responsible for identifying overdue invoices should not automatically receive permission to modify payment instructions.
Use Least-Privilege Access
Agents should receive only the permissions required for their assigned operations.
Read-only access is often appropriate during early deployment.
Write permissions can be introduced gradually after testing and validation.
Keep Critical Business Rules Deterministic
AI reasoning should not replace every conventional software rule.
Financial limits, regulatory restrictions, access policies, and equipment safety boundaries should be enforced through deterministic controls.
For example, an agent may recommend a purchase, but a separate policy engine should determine whether the amount exceeds an approval threshold.
Introduce Human Approval
Human-in-the-loop controls are important when an agent's actions may create financial, operational, legal, or safety consequences.
Approval workflows should clearly present the proposed action, supporting evidence, and expected impact.
Test Failure Scenarios
Testing should include more than successful task completion.
Organizations should evaluate how agents respond to unavailable APIs, incorrect records, conflicting instructions, expired credentials, and malicious content.
Tests should also cover repeated tool calls, duplicate transactions, and interrupted workflows.
Maintain Complete Audit Trails
Record the identity of the agent, its assigned task, tool interactions, policy decisions, approvals, and final outcomes.
Sensitive information should be protected through appropriate access controls and retention policies.
Common Pitfalls to Avoid
One common mistake is giving an agent broad permissions because it simplifies integration.
Another is deploying multiple agents before confirming that a single-agent workflow can reliably solve the problem.
Organizations also underestimate the importance of maintaining tool interfaces, evaluating model changes, and handling partial workflow failures.
Finally, many teams measure AI success using model response quality without checking whether the underlying business process actually improved.
Key takeaway: Build enterprise AI agents around controlled workflows, explicit permissions, reliable validation, and measurable business outcomes.
Performance, Cost, and Security Considerations
Enterprise AI agents introduce operating costs and security risks that differ from traditional applications.
A single user request may trigger multiple model calls, database queries, tool executions, and agent-to-agent interactions.
Without appropriate controls, these interactions can increase latency and operating costs.
Understanding AI Agent Costs
The total cost of an enterprise AI agent includes more than model inference.
Organizations should account for:
- Model usage and token consumption.
- Cloud compute and storage.
- Database and retrieval operations.
- API integration and maintenance.
- Monitoring and logging.
- Security controls.
- Human review and exception handling.
- Testing, evaluation, and ongoing support.
Consider a hypothetical deployment processing 100,000 tasks per month.
If each task requires four model calls, the system generates approximately 400,000 model calls monthly.
If workflow improvements reduce average model calls from four to two, the same workload requires approximately 200,000 calls.
This does not guarantee a 50% reduction in total cost because model sizes, token usage, infrastructure, and tool operations also matter.
However, it illustrates why workflow design can significantly affect operating economics.
Performance Optimization
Performance depends on model latency, tool response times, network conditions, and workflow complexity.
Sequential agent operations can create unnecessary delays.
Independent tasks may be executed concurrently when their dependencies and security requirements permit.
Caching can reduce repeated retrieval operations.
Smaller models may handle simple tasks more efficiently.
Deterministic software can replace model calls for predictable calculations and validations.
Organizations should measure end-to-end task completion time rather than only individual model response times.
Enterprise AI Agent Security
AI agents introduce additional security concerns because they can act on retrieved information.
One important threat is prompt injection.
An attacker may place malicious instructions inside a document, email, webpage, or tool response that an agent processes.
If the system fails to separate untrusted content from authorized instructions, the agent may attempt unintended actions.
Other risks include excessive permissions, sensitive data exposure, unauthorized tool execution, and compromised integrations.
The OWASP GenAI Security Project provides guidance on security risks associated with language-model applications and agentic systems.
Organizations can also use the NIST AI Risk Management Framework to structure AI risk assessment and governance activities.
Protecting Enterprise Systems
A secure architecture should separate model reasoning from privileged execution.
The agent may propose an action, but a trusted execution service should validate permissions and policy before carrying it out.
High-risk operations should require additional approval.
Credentials should remain in secure infrastructure rather than appearing directly in model prompts.
Sensitive data should be minimized before being sent to external models.
Monitoring should detect unusual tool usage, repeated failures, and unexpected access patterns.
Measuring Operational Performance
Useful enterprise AI metrics include task completion rate, human intervention rate, average execution time, cost per successful task, and unauthorized-action prevention.
Organizations should also measure the accuracy of completed business actions.
A workflow that completes quickly but frequently produces incorrect updates is not operationally successful.
If your organization is planning AI agent deployment, Infolitz can help review application integrations, infrastructure requirements, security boundaries, and operational monitoring needs before implementation.
Real-World Use Cases for Enterprise AI Agents
Enterprise AI agents can support many operational functions.
Their value is often greatest when a business process requires information from multiple systems and involves repetitive investigation or coordination.
Customer Support Operations
A customer support agent can retrieve account details, inspect previous interactions, review product documentation, and prepare responses.
With appropriate permissions, it may also create or update support tickets.
Complex complaints can be escalated to human employees.
The primary opportunity is reducing the time employees spend collecting information across disconnected systems.
IT Operations and Incident Management
An IT operations agent can analyze monitoring alerts, retrieve logs, compare incidents with historical records, and recommend troubleshooting actions.
For example, a cloud application may generate repeated database connection errors.
The agent could examine monitoring data, review recent deployment records, and prepare an incident summary.
However, restarting production services or modifying infrastructure should remain subject to defined policies and approvals.
Finance and Procurement
AI agents can assist with invoice verification, purchase-order matching, supplier communication, and exception identification.
They may retrieve information from accounting systems and supporting documents.
Financial approvals and payment execution should remain under deterministic controls.
Enterprise Knowledge Management
An internal knowledge agent can help employees find information across policies, technical documentation, and project records.
RAG can improve access to relevant material.
However, source permissions must remain enforced.
An employee should not gain access to confidential documents simply because an AI agent can retrieve them.
Industrial IoT and Predictive Maintenance
Industrial IoT is a particularly interesting application because AI agents can combine sensor information with maintenance workflows.
Traditional monitoring systems detect abnormal readings and generate alerts.
AI agents can help investigate what those alerts mean.
For example, an industrial motor may generate repeated vibration warnings.
A monitoring agent can retrieve recent sensor readings.
A diagnostic agent can compare those readings with historical patterns.
A maintenance agent can review service records.
An inventory agent can check replacement-part availability.
A scheduling agent can prepare a maintenance recommendation.
The resulting workflow connects equipment monitoring with operational planning.
However, safety-critical control actions should remain under validated industrial control systems rather than unrestricted language-model decisions.
Illustrative Mini Case Study: Industrial Equipment Monitoring
Consider a hypothetical manufacturer operating 250 connected industrial machines.
The company already collects temperature, vibration, and equipment-status data through an IoT platform.
Its monitoring system generates alerts when readings exceed predefined thresholds.
However, maintenance engineers must manually investigate each alert.
They review dashboards, compare historical readings, check maintenance records, and determine whether the alert requires immediate attention.
An AI-assisted workflow could reduce this investigation burden.
The proposed architecture would include an IoT data ingestion layer, equipment monitoring service, diagnostic agent, maintenance knowledge system, and human approval interface.
When an abnormal condition appears, the agent would retrieve relevant data, summarize possible causes, and prepare a recommended investigation.
Maintenance engineers would review the recommendation before authorizing physical intervention.
For illustration, suppose the organization processes 1,000 alerts monthly and currently spends an average of 12 minutes investigating each alert.
That represents approximately 200 staff-hours of investigation.
If a validated AI-assisted workflow reduced average investigation time to five minutes, the monthly effort would fall to approximately 83 staff-hours.
The potential reduction would be about 117 staff-hours per month.
These figures are hypothetical and illustrate a measurement approach, not results from an actual deployment.
The important point is that the agent does not need direct control of industrial machinery to provide operational value.
It can improve how information is collected, analyzed, and presented to responsible engineers.
AI Agents vs. Traditional Automation and Chatbots
AI agents are not replacements for every existing automation technology.
Different approaches solve different types of problems.
Traditional Automation
Traditional automation follows predefined rules.
For example, when an invoice is approved, a workflow may update an accounting system and send a notification.
This approach is predictable and often easier to test.
It works well when inputs and decisions follow stable rules.
Robotic Process Automation
Robotic process automation, or RPA, automates repetitive interactions with software interfaces.
It can be useful when applications lack suitable APIs.
However, interface changes and unexpected input formats can make RPA workflows fragile.
AI Assistants
AI assistants primarily support users through conversational interactions.
They may answer questions, summarize documents, or generate content.
Some assistants also have tool access, so the distinction between assistants and agents is not absolute.
The practical difference lies in the degree of independent task execution.
Autonomous AI Agents
AI agents can select tools and coordinate multiple steps toward a defined objective.
This flexibility can help with workflows involving uncertain information or changing conditions.
However, it also introduces additional complexity.
The system must validate actions, manage permissions, handle failures, and maintain accountability.
Multi-Agent Systems
Multi-agent systems distribute responsibilities across several specialized agents.
This can improve modularity when tasks require distinct capabilities or ownership boundaries.
However, additional agents create more communication, coordination, and debugging overhead.
A multi-agent architecture is not automatically more effective than a single-agent system.
When Should Enterprises Use AI Agents?
Use conventional automation when the process is predictable and rule-based.
Consider AI-assisted workflows when tasks involve language interpretation, document analysis, or information retrieval.
Consider autonomous agents when tasks require flexible tool selection and multi-step coordination, and when the organization can enforce appropriate safeguards.
Use multiple agents when specialization or independent responsibilities provide a clear operational benefit.
How to Prepare Your IT Architecture for AI Agents
Organizations do not necessarily need to rebuild their existing technology infrastructure.
A gradual approach is often more practical.
Step 1: Identify Suitable Workflows
Begin by reviewing processes that require repetitive investigation, information gathering, or coordination.
Prioritize workflows with measurable outcomes and manageable consequences if something goes wrong.
Step 2: Review Existing Systems
Identify the applications, databases, APIs, and documents required by the selected workflow.
Evaluate whether existing systems expose reliable interfaces.
Legacy applications may require adapters or controlled integration services.
Step 3: Define Security Boundaries
Determine which data and operations the agent may access.
Create dedicated agent identities and enforce least-privilege permissions.
Separate read-only operations from actions that modify business records.
Step 4: Choose the Execution Architecture
Decide whether the workflow requires a single agent, multiple agents, or a combination of conventional automation and AI.
Select models and frameworks based on functional requirements.
Step 5: Build a Controlled Pilot
Begin with a limited set of users, systems, and tasks.
Use test environments and representative data.
Where practical, run agents in observation mode before enabling write operations.
Step 6: Evaluate Results
Measure task accuracy, completion time, operating cost, human intervention, and security events.
Compare results against the existing process.
Step 7: Expand Gradually
Introduce additional workflows only after the initial deployment demonstrates acceptable reliability.
Increase permissions cautiously.
Maintain testing, monitoring, and governance as the system evolves.
This approach helps organizations avoid unnecessary infrastructure changes while learning where AI agents provide measurable value.

FAQs
1. What is AI Agent Architecture for Enterprises?
AI Agent Architecture for Enterprises is the framework used to connect AI agents with business applications, data sources, APIs, and workflows. It includes orchestration, model execution, integration, security, monitoring, and governance components.
2. How do enterprise AI agents work?
Enterprise AI agents receive objectives, interpret information, select approved tools, and execute tasks through connected systems. Their actions should remain subject to access controls, validation, and human approval when necessary.
3. What is the difference between AI agents and AI assistants?
AI assistants primarily help users retrieve information or generate responses. AI agents can also coordinate multi-step workflows and execute approved actions. The distinction depends on system capabilities and the autonomy granted.
4. What infrastructure is required for AI agents?
Typical infrastructure includes model access, orchestration services, enterprise APIs, identity management, secure data access, logging, monitoring, and policy enforcement. The exact requirements depend on the workflow and deployment environment.
5. Can AI agents work with legacy enterprise systems?
Yes. AI agents can interact with legacy systems through APIs, integration middleware, database services, or controlled automation interfaces. The reliability and security of these integrations must be evaluated before production deployment.
6. What is multi-agent architecture?
Multi-agent architecture uses multiple specialized AI agents to perform different parts of a workflow. An orchestration mechanism coordinates responsibilities, communication, and task completion.
7. How can enterprises secure autonomous AI agents?
Enterprises should implement dedicated agent identities, least-privilege access, tool authorization, input validation, audit logging, and human approval for sensitive actions. Untrusted content must not be allowed to override system instructions or security policies.
8. What is the role of MCP in enterprise AI?
Model Context Protocol provides standardized interfaces for connecting AI applications with external tools and information sources. It can simplify integration, but organizations must still implement appropriate authentication, authorization, and security controls.
9. Can AI agents integrate with IoT systems?
Yes. AI agents can retrieve sensor data, analyze alerts, access equipment documentation, and coordinate maintenance workflows. Safety-critical equipment commands should remain protected by validated control systems and appropriate human oversight.
10. How much does enterprise AI agent deployment cost?
Costs depend on model usage, workflow complexity, infrastructure, integrations, security requirements, and ongoing maintenance. Organizations should evaluate cost per successfully completed business task rather than model pricing alone.
AI agents are moving from answering questions to executing business tasks. The real challenge is no longer making AI intelligent, but building enterprise systems that can trust, control, and monitor its actions

Conclusion
AI agents are becoming capable of performing work that previously required employees to move between applications, retrieve information, and coordinate multiple operational steps.
However, enterprise adoption requires more than powerful language models.
Organizations need architecture that establishes agent identity, controls access, connects existing systems, validates actions, monitors performance, and preserves human accountability.
The strongest starting point is not a large autonomous AI workforce. It is a clearly defined business workflow where AI can deliver measurable improvement without introducing unacceptable operational risk.
As agent capabilities evolve, organizations with secure, modular, and observable architectures will be better positioned to adopt them responsibly.
Build an Enterprise Architecture Ready for AI Agents
Preparing for enterprise AI agents starts with understanding your existing systems, integration requirements, and operational risks.
Infolitz Software Pvt. Ltd. helps organizations design and develop connected applications, cloud platforms, IoT solutions, and AI-enabled systems.
If you are exploring enterprise AI agents or planning to integrate AI capabilities into your existing technology stack, contact Infolitz Software to discuss your requirements.


