
MCP Explained: Why Enterprises Need a Standard Way for AI to Access Tools

Enterprise AI is moving beyond chat.
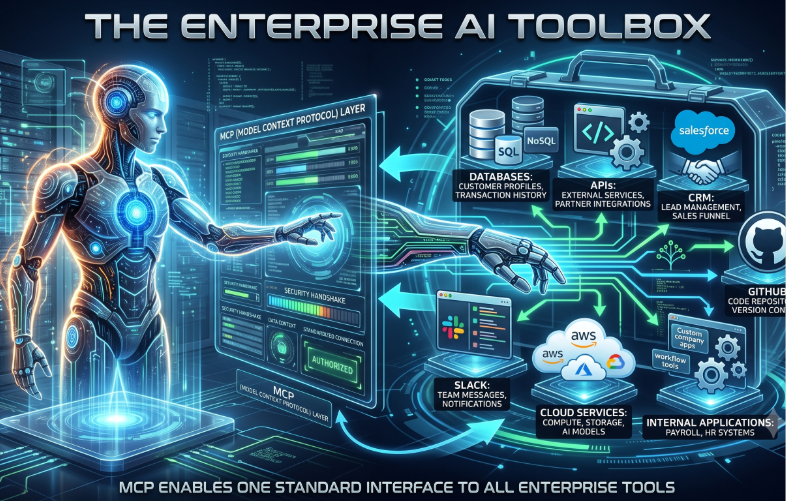
Organizations increasingly want AI assistants and agents to retrieve customer records, inspect operational data, search internal documents, query databases, create tickets, analyze telemetry, update business systems, and trigger workflows.
That creates a problem.
If every AI application requires its own custom integration with every enterprise system, companies can quickly end up maintaining dozens of separate connections.
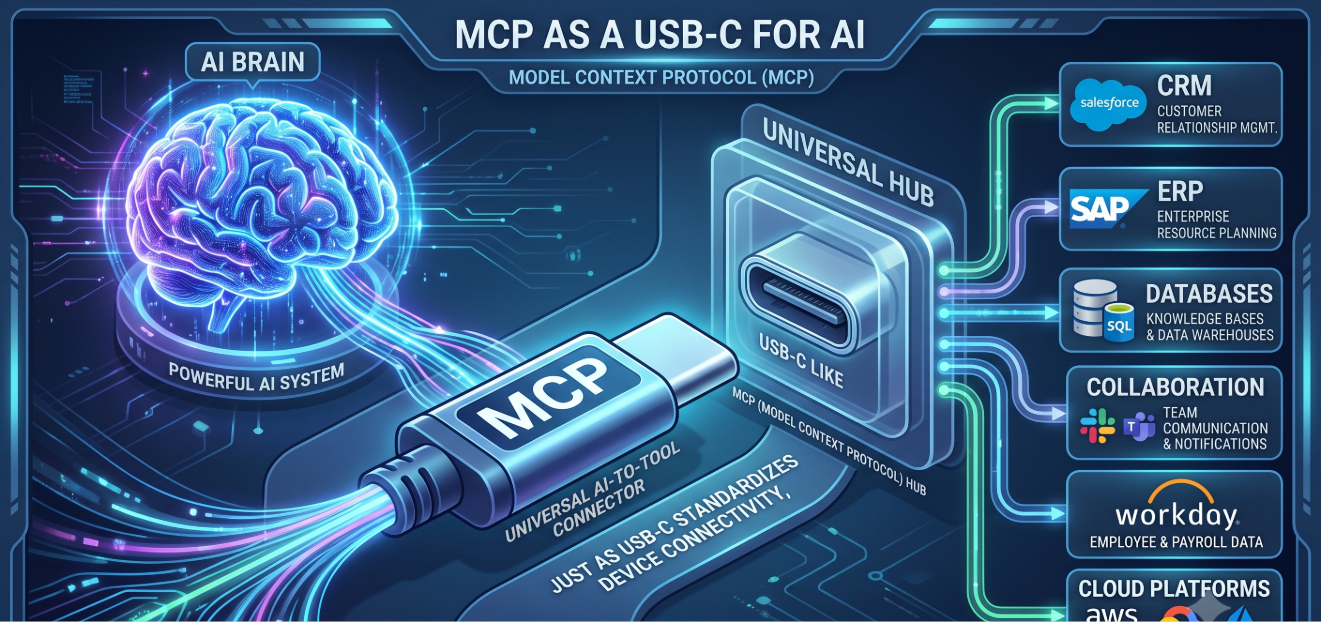
Model Context Protocol (MCP) offers another approach.
Instead of defining a different integration pattern for every AI application, MCP provides a standardized way for AI applications to discover and use external tools, resources, and services. The current MCP SDK documentation describes MCP as an open standard connecting AI applications to systems where tools and data live.
For enterprises, the important question is not simply what MCP is.
It is whether MCP can become a controlled integration boundary between AI and the systems where work actually happens.
What Is Model Context Protocol?
Model Context Protocol is an open standard that enables AI applications to connect with external tools, data sources, and services through a common interface.
Think about a typical enterprise environment.
A company may operate:
- CRM software
- ERP systems
- document repositories
- cloud platforms
- IoT platforms
- ticketing applications
- source-code repositories
- analytics systems
- internal databases
- proprietary applications
An AI assistant cannot automatically understand how to interact with all of them.
Traditionally, developers create individual integrations.
The CRM has one API.
The ticketing system has another.
The IoT platform has its own endpoints.
The database uses another interface.
Then every AI application needs orchestration code to understand those systems.
MCP introduces a standardized AI-facing layer.
At a simplified level:
AI Application → MCP → Enterprise Systems
Underneath, the enterprise can continue using the APIs, databases, services, and business logic it already has.
That distinction matters.
MCP does not replace your enterprise systems. It standardizes how AI applications can discover and interact with approved capabilities.
Why Enterprises Need a Standard Way for AI to Access Tools
Imagine a company operating five AI applications.
Those applications need access to ten enterprise systems.
Without reusable integration layers, teams may face dozens of AI-to-system integration relationships.
Now add another AI assistant.
Or replace the current model provider.
Or introduce a specialized coding agent.
The integration surface keeps growing.
The engineering problem is only one part of it.
Every integration raises questions about:
- authentication
- authorization
- credential management
- input validation
- output validation
- logging
- auditing
- error handling
- versioning
- monitoring
- user permissions
MCP can move organizations away from an architecture where each AI application understands each system independently.
Instead of:
AI Assistant A → custom CRM integration
AI Assistant B → another CRM integration
AI Agent C → another CRM integration
the organization can expose carefully defined CRM capabilities through an MCP server.
Compatible AI applications can then discover those capabilities through the protocol.
That creates the potential for integration reuse.
It also creates a clearer place to apply enterprise controls.
The benefit becomes increasingly important as organizations move from one AI experiment to multiple agents and applications.
How MCP Works
The basic MCP architecture is easier to understand when divided into four components.
MCP Host
The host is the AI application where the user or agent operates.
It could be:
- an enterprise AI assistant
- a coding environment
- an internal copilot
- an AI operations interface
- a custom agent application
The host manages the overall AI experience.
MCP Client
The client manages communication between the host and MCP servers.
A host can potentially connect to multiple servers, each providing different capabilities.
MCP Server
The MCP server exposes approved functionality.
The official MCP SDKs allow servers to expose tools, resources, and prompts.
An enterprise might therefore operate separate servers for:
- CRM
- support
- IoT
- engineering
- analytics
- internal knowledge
Enterprise Systems
Behind the MCP server are the systems the business already uses.
The MCP server might call:
- REST APIs
- internal services
- databases
- cloud functions
- enterprise applications
- IoT APIs
A useful mental model is:
User → AI Host → MCP Client → MCP Server → Existing API → Business System
The MCP server becomes the AI-facing capability layer.
Tools, Resources, and Prompts
Three MCP concepts are particularly useful for understanding what an MCP server exposes.
Tools
Tools allow models to request actions or computations.
Examples might include:
find_customer
get_device_status
create_support_ticket
check_inventory
get_monthly_sales
restart_device
The last example illustrates an important security distinction.
Reading device status is relatively low risk.
Restarting a production device is not.
The two tools should therefore have different authorization and approval policies.
Resources
Resources expose information that applications or models can consume.
These might include documentation, configuration information, application data, knowledge sources, or other contextual information.
Prompts
Prompts are reusable message templates that can support structured workflows. Current MCP documentation distinguishes them from tools: tools are intended for model-driven invocation, while prompts are typically user-selected templates.
MCP Tools and Stack Options
Enterprises have several choices when building an MCP implementation.
The official MCP ecosystem currently includes stable SDK support across major development environments. The TypeScript and Python SDKs implement the current 2026-07-28 specification.
TypeScript
A strong choice for organizations already operating Node.js or TypeScript services.
It works particularly well where MCP servers need to integrate with web applications, existing APIs, or JavaScript-based infrastructure.
Python
A natural fit for AI-heavy environments, data platforms, machine-learning systems, and Python-based backend services.
Java
Useful in organizations with significant enterprise Java infrastructure, including Spring-based applications.
The Java MCP SDK provides server-side capabilities including tools, resources, prompt templates, capability negotiation, logging, and concurrent client support.
Go and other ecosystems
MCP continues to expand across languages and frameworks. The correct choice should usually follow your existing engineering environment rather than introducing a new language solely for MCP.
Existing APIs
For many enterprises, the most practical architecture will be:
AI → MCP → Existing API → Existing System
This allows companies to preserve business logic and validation already implemented in their service layer.
Direct Database Integration
MCP servers can technically interact with databases.
That does not mean they always should.
Existing service layers often provide stronger:
- authorization
- validation
- business rules
- observability
- maintainability
Direct database access should therefore be a deliberate architectural decision rather than the default.
Enterprise MCP Best Practices
A working MCP server is not automatically a production-ready MCP server.
Before connecting AI agents to enterprise systems, establish a clear control model.
Start Read-Only
Begin with operations such as:
- search documentation
- retrieve customer information
- inspect device status
- query analytics
- retrieve inventory
- analyze logs
Read-heavy use cases let teams validate the architecture before introducing actions that change business systems.
Apply Least Privilege
Each MCP server should receive only the permissions required for its specific purpose.
OWASP recommends narrow OAuth scopes, per-server credentials, minimum permissions, and short-lived credentials where practical.
A support knowledge server does not need permission to modify production infrastructure.
Separate Read and Write Operations
Consider separating:
device.read
from:
device.restart
or:
customer.read
from:
customer.update
This makes policy enforcement easier.
Require Human Approval for Sensitive Actions
Sensitive operations should not happen simply because an LLM generated the correct tool call.
OWASP recommends explicit user confirmation for destructive, financial, and data-sharing operations.
Examples include:
- deleting records
- transferring funds
- modifying production systems
- sending external communications
- changing permissions
- controlling physical equipment
Validate Inputs
LLM-generated parameters are still untrusted inputs.
Every tool should validate its parameters before passing them to an underlying application.
Validate Outputs
The opposite direction matters too.
Information returned by tools can contain malicious or misleading instructions.
OWASP specifically warns about prompt injection through MCP tool responses and recommends treating tool outputs as untrusted input.
Log Tool Activity
For consequential operations, enterprises should be able to answer:
Who requested the action?
Which AI application initiated it?
Which MCP server received it?
Which tool executed?
What parameters were supplied?
What was the result?
Was approval required?
Enterprise MCP Checklist
Before production deployment, confirm that you have:
- defined narrow tool boundaries
- applied least-privilege permissions
- separated sensitive actions
- implemented authentication
- implemented authorization
- validated tool inputs
- validated tool outputs
- protected credentials
- added human approval where necessary
- implemented audit logging
- monitored unusual tool activity
- defined ownership for each server
- tested prompt-injection scenarios
- reviewed third-party MCP dependencies
Performance, Cost, and Security Considerations
Performance
MCP adds another layer to the request path.
For many enterprise AI workflows, model inference and backend processing will dominate the overall response time.
But not every workload belongs behind an AI agent.
Consider an industrial system making control decisions every few milliseconds.
That workflow probably should not depend on an LLM deciding which MCP tool to call.
MCP is better suited to tasks where reasoning, interpretation, or human interaction adds value.
For example:
“Show me all pumps with repeated vibration alerts during the last seven days and summarize the likely maintenance priority.”
That is a strong AI-assisted workflow.
A real-time emergency shutdown loop is not.
Cost
Organizations should avoid evaluating MCP only through server hosting costs.
The larger cost includes:
- integration development
- security engineering
- identity management
- observability
- testing
- maintenance
- model usage
- operational support
The economic question should be:
How many reusable integrations and workflows does this architecture enable?
If one MCP server supports multiple AI applications, integration reuse may become meaningful.
Security
MCP creates a powerful integration surface, which also creates a new attack surface.
OWASP identifies risks including tool poisoning, tool shadowing, excessive permissions, confused-deputy problems, prompt injection, supply-chain attacks, and data exfiltration.
The MCP specification has also continued strengthening enterprise authorization.
The July 2026 specification introduced further authorization hardening and moved the core toward a stateless request-response model that works more naturally with ordinary HTTP infrastructure, gateways, rate limiters, and web application firewalls.
Enterprise-Managed Authorization also reached stable status in June 2026. It allows organizations to centrally provision MCP server access through their identity infrastructure rather than forcing users through separate authorization flows for every application.
Real-World MCP Use Cases
IT Support
Imagine an employee reports:
“My VPN keeps disconnecting.”
An enterprise AI assistant could use approved tools to:
- retrieve device details
- check recent network incidents
- search support documentation
- inspect previous tickets
- create a new ticket
The employee interacts with one assistant while MCP provides standardized access to the underlying capabilities.
Customer Service
A customer asks:
“Where is my order, and why was it delayed?”
The AI might need information from:
- CRM
- order management
- logistics
- customer support
- product documentation
MCP can provide controlled access to each source without requiring the model to contain that information.
Software Development
Coding agents may need access to:
- repositories
- issue trackers
- technical documentation
- development environments
- testing systems
- deployment infrastructure
Production deployment tools should naturally receive stricter permissions than documentation search.
Data Analytics
A business manager asks:
“Which regions had the highest increase in service failures this month?”
The AI can retrieve approved datasets, analyze them, and explain the result.
The model does not need unrestricted database credentials.
It needs the correct tools.
IoT Operations
MCP is particularly interesting for connected-product environments.
An operations engineer could ask:
“Which devices have been offline for more than six hours?”
An IoT MCP server might expose:
- device status
- telemetry history
- firmware versions
- connectivity diagnostics
- configuration information
- alert history
A separate tool could create maintenance tickets.
Another could initiate a remote restart, but only after explicit approval.
This combination of AI + MCP + IoT can turn dashboards into more conversational operational workflows.
Mini Case Study: From Five Systems to One AI Workflow
Consider a hypothetical industrial equipment company.
Its service engineers use five separate systems:
an IoT monitoring platform, CRM, ticketing application, asset-management platform, and internal documentation portal.
When equipment fails, an engineer starts by identifying the customer.
Then they open the IoT dashboard.
Next comes asset history.
Then documentation.
Finally, the engineer opens the ticketing platform.
Assume this initial information-gathering process takes 15 minutes per incident.
Across 40 incidents per day, that represents approximately 10 staff-hours spent gathering context before deeper troubleshooting begins.
Now imagine the company creates an internal AI operations assistant.
Instead of giving the assistant broad access to every system, the company exposes a small set of approved MCP tools:
get_customer_asset
get_device_health
get_recent_alerts
get_service_history
search_documentation
prepare_support_ticket
An engineer can now ask:
“Summarize the current condition and service history for Asset 2871.”
The AI retrieves approved information from multiple systems.
It returns:
- customer information
- current device state
- recent alarms
- firmware version
- previous service history
- related support cases
The engineer then asks:
“Prepare a diagnostic ticket with this information.”
The system prepares the action.
The engineer reviews it.
Only then is the ticket created.
The important improvement is not that an AI model gained unrestricted access.
It is that the company converted existing systems into small, controlled capabilities that AI applications can reuse.
If the workflow reduced information gathering from 15 minutes to five minutes, the company would save roughly 6.7 staff-hours across those 40 daily incidents.
That is the type of operational metric an MCP pilot should measure.
MCP vs Traditional APIs
MCP does not make APIs obsolete.
Traditional APIs remain excellent for deterministic software-to-software communication.
Your CRM API knows how to retrieve customer information.
Your IoT API knows how to retrieve telemetry.
Your ticketing API knows how to create tickets.
Those capabilities do not disappear.
MCP can sit above them.
An API essentially answers:
“How does software interact with this service?”
MCP addresses another problem:
“How can AI applications discover and use approved capabilities through a standardized interface?”
For many enterprises, the architecture will therefore look like:
AI → MCP → API → Enterprise System
Use APIs when building deterministic application integrations.
Consider MCP when capabilities need to be exposed consistently to multiple AI applications or agents.
MCP vs Function Calling
Function calling allows an AI model to request predefined functions from the application orchestrating it.
It remains extremely useful.
MCP addresses a broader interoperability problem.
With function calling alone, the application typically owns its tool definitions and integration logic.
MCP allows external servers to expose capabilities through a standard protocol.
That makes reuse across compatible AI applications more practical.
The technologies can also work together.
An AI host may use its model's function or tool-calling capabilities to decide what action is required while MCP provides the standardized infrastructure for discovering and invoking external capabilities.
So the decision is not necessarily:
MCP or function calling?
It can be:
Function calling within the model interaction + MCP for standardized external integration.
When MCP May Not Be Necessary
Not every enterprise AI project requires MCP.
Suppose you have one AI application.
It calls one stable internal API.
The integration is simple, secure, and unlikely to be reused.
Adding MCP may simply introduce another layer.
Now consider another environment:
10 AI applications.
30 enterprise systems.
Multiple model providers.
Hundreds of reusable capabilities.
Strict security and audit requirements.
In that environment, standardization becomes much more valuable.
MCP is most compelling when organizations face:
- multiple AI applications
- many business systems
- reusable enterprise capabilities
- multiple agent frameworks
- portability requirements
- centralized governance
- complex identity requirements
Where MCP Is Heading
MCP is evolving rapidly.
The current 2026-07-28 specification introduced a stateless protocol core, cacheable list results, header-based routing, authorization hardening, and an extensions framework.
The stateless direction is particularly relevant for enterprises because it allows MCP infrastructure to work more naturally with standard HTTP infrastructure such as gateways, load balancers, rate limiters, and web application firewalls.
The latest MCP roadmap also identifies continued work around areas such as agent identity, delegation, governance, and enterprise readiness.
That is worth remembering.
MCP is increasingly enterprise-oriented, but it remains an evolving ecosystem.
Companies should therefore design MCP implementations with versioning, replaceability, and clear abstraction boundaries.
Do not hardwire your entire enterprise architecture to today's implementation assumptions.
FAQs
What is Model Context Protocol?
Model Context Protocol is an open standard for connecting AI applications with external tools, resources, data, and services through a standardized interface.
Why do enterprises need MCP?
Enterprises may have many AI applications and many business systems. MCP can reduce duplicated integration logic by providing a reusable interface through which AI applications discover and invoke approved capabilities.
What is an MCP server?
An MCP server exposes capabilities that MCP clients can discover and use. These can include tools, resources, and prompts.
Does MCP replace APIs?
No. MCP servers can call existing APIs behind the scenes. Traditional APIs remain important for application integration, while MCP provides an AI-facing interoperability layer.
What is MCP vs function calling?
Function calling allows a model to request functions provided by its application. MCP standardizes how external systems expose capabilities to compatible AI applications. They can be used together.
Is MCP secure for enterprises?
MCP can be part of a secure enterprise architecture, but the protocol alone does not make a system secure. Organizations still need authentication, authorization, least privilege, input and output validation, monitoring, auditing, and approval controls for sensitive actions.
Can MCP connect to internal enterprise applications?
Yes. Organizations can build MCP servers around existing APIs, databases, internal services, cloud applications, IoT platforms, and other enterprise systems.
Can MCP be used with IoT?
Yes. An MCP server can expose device telemetry, status, diagnostics, configuration, alerts, and operational actions to an AI application. Sensitive device-control operations should have stricter permissions and approval requirements.
Should an MCP server connect directly to a database?
It can, but direct database access is not always the best architecture. Existing service or API layers often provide better validation, business-rule enforcement, authorization, and observability.
How should an enterprise start implementing MCP?
Choose one bounded workflow.
Start with three to five read-oriented capabilities.
Connect them through existing APIs where practical.
Apply least privilege.
Log every tool invocation.
Measure whether the workflow improves.
Only then add more systems or write operations.
The challenge with enterprise AI is no longer just what the model knows. It is what the model can safely access, understand, and act on.

Conclusion
The Future of Enterprise AI Depends on Controlled Access
Enterprise AI is moving from answering questions to interacting with the systems where real work happens.
That shift creates a new architectural challenge. Giving every AI assistant or agent its own custom connection to CRM platforms, databases, IoT systems, ticketing tools, and internal applications will become increasingly difficult to maintain and govern.
Model Context Protocol offers a more standardized approach. It can provide a common layer through which AI applications discover and use approved enterprise capabilities while existing APIs and business systems continue doing what they already do well.
But MCP should not be treated as a shortcut to unrestricted AI access.
The strongest enterprise implementations will combine MCP with identity, least privilege, clear tool boundaries, human approval for sensitive actions, monitoring, and audit trails.
Building an AI assistant or agent that needs to work with your existing applications, APIs, data, or IoT infrastructure requires more than connecting an LLM.
Talk to Infolitz about designing a secure, practical MCP and enterprise AI integration architecture around the systems you already operate.


