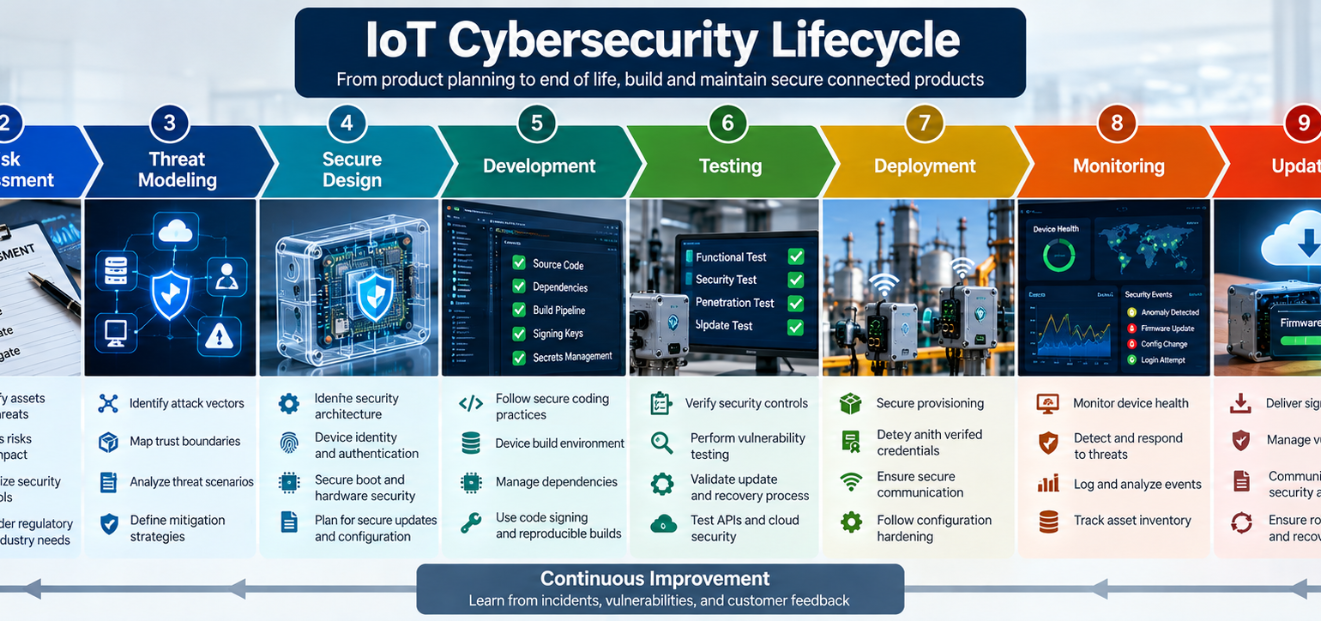

NIST Updated Its IoT Cybersecurity Guidance: What Manufacturers Should Change

Building a secure IoT device is no longer enough.
A connected product may include embedded firmware, Wi-Fi or cellular connectivity, mobile applications, gateways, APIs, cloud infrastructure, device management platforms, databases, and third-party services. A vulnerability in any one of those layers can undermine the security of the entire product.
NIST has now updated its foundational manufacturer guidance to reflect that reality.
The final NIST IR 8259 Revision 1, Foundational Cybersecurity Activities for IoT Product Manufacturers, was published in April 2026 and supersedes the original 2020 NIST IR 8259. The revision gives manufacturers a broader product and lifecycle perspective on IoT cybersecurity.
For manufacturers, the practical question is therefore not simply, "Are our devices secure?"
It is:
Can we keep the entire connected product securable from product planning through deployment, operation, vulnerability remediation, and end of life?
That change has significant implications for how IoT products should now be designed and supported.
What Is NIST IR 8259 Rev. 1?
NIST IR 8259 Rev. 1 provides foundational cybersecurity activities for organizations manufacturing IoT products.
The original NIST IR 8259, published in 2020, concentrated heavily on helping manufacturers create securable IoT devices. The new revision explicitly takes a broader IoT product perspective.
NIST describes an IoT product as potentially including not only the connected device, but also related components such as gateways, companion applications, and cloud backends.
That distinction matters.
Consider a connected industrial monitoring system.
The complete product might contain:
- Sensors installed on equipment
- Embedded firmware
- An edge gateway
- Ethernet, Wi-Fi, BLE, or cellular connectivity
- MQTT or HTTPS communication
- Device management software
- Cloud APIs
- Databases
- A web dashboard
- A mobile application
- Firmware update infrastructure
Securing only the sensor firmware leaves significant portions of the attack surface untouched.
NIST's revised approach encourages manufacturers to consider cybersecurity across that entire ecosystem.
Why Did NIST Update Its IoT Cybersecurity Guidance?
Connected products have changed significantly since the original guidance appeared in 2020.
Modern IoT architectures increasingly depend on cloud platforms, APIs, mobile applications, third-party libraries, remote management systems, identity services, and long-lived software components.
At the same time, many IoT products remain deployed for years or even decades.
NIST specifically notes that IoT products may stay in service for decades and may operate under constraints such as limited computing resources, cost restrictions, high latency, extreme temperature, or high humidity.
Those characteristics create a difficult cybersecurity problem.
A product may leave the factory secure today but become vulnerable several years later because:
- A software dependency develops a vulnerability.
- Cryptographic practices change.
- A cloud API is exposed incorrectly.
- Credentials are compromised.
- A third-party component stops receiving updates.
- Attack techniques evolve.
- The manufacturer stops supporting the product.
Cybersecurity therefore cannot end when manufacturing ends.
It has to become part of product lifecycle management.
The Biggest Change: Think Product, Not Device
One of the most useful ideas in the revised guidance is simple:
The security boundary should follow the product, not just the hardware enclosure.
A manufacturer might previously have reviewed:
MCU → Firmware → Network Interface
A modern assessment should look more like:
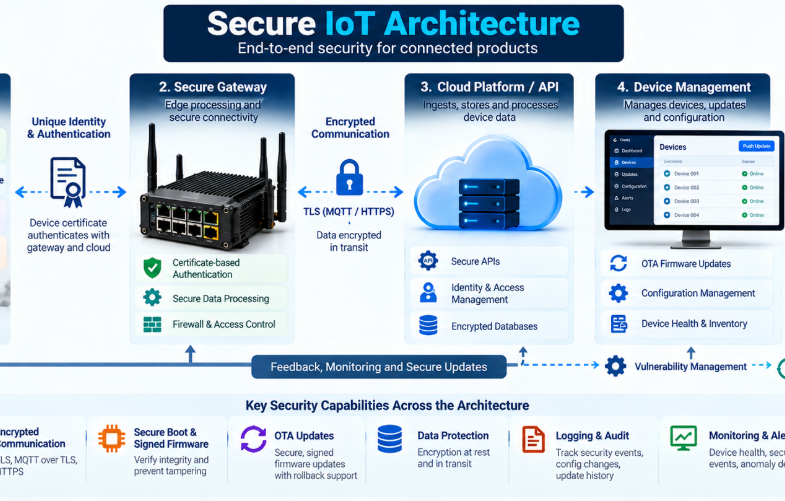
Device → Firmware → Gateway → Network → API → Cloud → Database → Application → Operations
NIST's own IoT program explains that customers generally expect the complete product to be secure rather than distinguishing between the device and the supporting cloud, application, or gateway components.
For engineering teams, this changes architecture reviews.
A firmware security review is still necessary, but it is no longer sufficient.
Teams should also ask:
- How does the device authenticate to the cloud?
- How does the cloud authenticate the device?
- What happens when credentials are compromised?
- Who can change device configuration?
- Which interfaces are exposed?
- How are APIs protected?
- What gets logged?
- Can compromised devices be isolated?
- Can software be updated safely?
- What happens if the cloud service is discontinued?
Those questions should increasingly appear in product requirements, not only security audits.
How the Updated NIST Model Works
NIST IR 8259 Rev. 1 organizes its recommendations into nine foundational activities.
Six primarily concern the pre-market phase, while three focus primarily on post-market responsibilities.
Before the product reaches the market
Manufacturers should:
- Prioritize cybersecurity and maintain the organization's cybersecurity posture.
- Identify expected customers and define expected use cases.
- Research customer cybersecurity needs and goals.
- Determine appropriate ways to support those needs within the context of the IoT product.
- Define IoT product cybersecurity capabilities.
- Plan adequate support for customer cybersecurity needs.
After the product reaches the market
Manufacturers should:
- Provide ongoing cybersecurity support throughout the product lifecycle and end of life.
- Define how cybersecurity information will be communicated to customers.
- Determine what cybersecurity information customers need and how it should be communicated.
This structure makes an important point.
Cybersecurity does not belong to one security engineer at the end of development.
It affects product management, embedded engineering, cloud development, DevOps, QA, customer support, legal teams, operations, and product leadership.
NIST also intentionally avoids mapping these activities to a particular organizational structure because manufacturers differ in how responsibilities are divided.
What Should IoT Manufacturers Change?
1. Move security into product planning
The first major change should happen before architecture is finalized.
Cybersecurity requirements should become part of product requirements alongside performance, cost, connectivity, battery life, and usability.
For example, instead of writing:
Device must support remote firmware updates.
Engineering requirements should ask:
- Who is authorized to trigger an update?
- How is firmware authenticity verified?
- Is firmware digitally signed?
- What happens if an update fails?
- Can the device safely recover?
- Can vulnerable versions be blocked?
- Can update status be audited?
These decisions become much harder to retrofit after thousands of devices have already shipped.
NIST explicitly emphasizes beginning cybersecurity during product planning, when decision-makers can allocate resources to threat modeling, prioritization, and security capabilities.
2. Add formal threat modeling
NIST's revision places stronger emphasis on cybersecurity risk assessment and threat modeling. During the revision process, NIST specifically expanded attention to risk assessment and threat modeling as part of product development.
That means manufacturers should stop treating threat modeling as something reserved for highly regulated products.
For a connected machine, the team might examine threats involving:
- Physical device access
- Debug interfaces
- Firmware extraction
- Credential theft
- Device impersonation
- API abuse
- Malicious firmware
- Man-in-the-middle attacks
- Cloud account compromise
- Privilege escalation
- Gateway compromise
- Supply chain components
- Denial-of-service attacks
The output does not need to become a hundred-page security document.
The important outcome is understanding:
What can go wrong, how serious would it be, and what controls reduce that risk?
3. Secure the development environment too
An IoT product can contain strong cryptography and still be compromised if attackers gain access to its build pipeline.
Manufacturers should therefore assess the systems used to build and deliver the product.
That includes:
- Source code repositories
- Developer accounts
- CI/CD pipelines
- Signing keys
- Firmware build systems
- Artifact repositories
- Cloud deployment credentials
- Third-party dependencies
NIST's updated material references secure software development practices and software supply chain risk management, including connections to the Secure Software Development Framework and NIST SP 800-161 Rev. 1.
For IoT teams, this is especially important because a compromised firmware signing process could potentially affect an entire deployed fleet.
4. Strengthen device identity
A manufacturer should be able to answer:
Which exact device is connecting to our platform?
Generic credentials shared across thousands of products create unnecessary risk.
A stronger architecture normally gives every device a unique identity.
Depending on the product, this may involve:
- Unique device certificates
- Securely provisioned credentials
- Hardware-backed key storage
- Per-device authentication
- Credential rotation
- Device revocation
This also improves fleet operations.
Once identity becomes reliable, manufacturers can associate security events, firmware versions, configuration state, ownership, and device health with individual assets.
5. Control device configuration
Configuration is often overlooked as a cybersecurity capability.
IoT products may expose configuration through:
- Local web interfaces
- BLE
- Serial interfaces
- Mobile apps
- Cloud dashboards
- APIs
- Remote management systems
Manufacturers should determine exactly who can change each setting.
The principle should be straightforward:
Only authorized entities should be able to modify security-sensitive configuration.
NIST IR 8259A identifies device configuration as one of the core IoT cybersecurity capabilities.
6. Make secure updates a product capability
Every manufacturer should assume that vulnerabilities will eventually be discovered.
The question is whether the product can respond safely.
A mature update process should consider:
- Firmware authenticity
- Digital signatures
- Encrypted transport where appropriate
- Version control
- Rollback behavior
- Failed-update recovery
- Update authorization
- Device compatibility
- Update logging
- Long-term availability
Secure updates are therefore not simply a DevOps feature.
They are part of the security architecture of the product.
If your current IoT architecture was designed mainly around getting telemetry from devices into the cloud, reviewing authentication, update management, configuration control, and lifecycle support can reveal security gaps before they become expensive field problems.
Tools and Stack Options
There is no single mandatory technology stack for implementing NIST guidance.
The correct controls depend on the device's capabilities, operating environment, risk level, and customer needs.
Device security options
Common technologies include:
- Secure boot
- Hardware root of trust
- TPM or secure element
- Signed firmware
- Flash encryption
- Protected key storage
- Debug-port controls
- Unique device credentials
Communication security
Typical options include:
- TLS
- Mutual TLS
- MQTT over TLS
- HTTPS
- Certificate-based authentication
- VPNs for specific industrial deployments
Cloud and platform controls
Manufacturers may use:
- Identity and access management
- Secrets management
- Certificate management
- API gateways
- Centralized logging
- Security monitoring
- Device registries
- Fleet management platforms
Development security
The software pipeline may include:
- Static application security testing
- Dependency scanning
- Software composition analysis
- Secrets scanning
- Container scanning
- CI/CD security controls
- Signed build artifacts
The important point is not to deploy every available cybersecurity tool.
NIST uses a risk-based approach. Manufacturers should choose controls that match their product, environment, customers, and threats.
Best Practices for Implementing the Guidance
A practical implementation program should include the following.
During product definition
- Identify expected customers.
- Document intended deployment environments.
- Identify regulatory and contractual requirements.
- Define expected product lifetime.
- Identify security assumptions.
During architecture
- Map the complete connected product.
- Identify trust boundaries.
- Document every network interface.
- Define device identity.
- Define authentication flows.
- Perform threat modeling.
During development
- Protect source repositories.
- Secure build pipelines.
- Manage secrets centrally.
- Review third-party dependencies.
- Implement secure boot where appropriate.
- Implement secure update mechanisms.
Before release
- Perform penetration testing where warranted.
- Verify firmware update behavior.
- Review cloud permissions.
- Validate API authentication.
- Confirm logging and monitoring.
- Document security configuration.
After deployment
- Monitor vulnerabilities.
- Maintain supported software versions.
- Investigate security incidents.
- Communicate material security issues.
- Maintain update capability.
- Track approaching end-of-life dates.
NIST's model extends from pre-market product conception through product retirement, making post-market security an explicit part of the lifecycle.
Common IoT Cybersecurity Pitfalls
Treating cybersecurity as a final QA activity
Security testing shortly before launch may find problems, but architecture-level issues can be expensive to correct at that stage.
Threat modeling should happen earlier.
Protecting the cloud but trusting the device
Attackers may have physical access to deployed IoT products.
Firmware, credentials, debug interfaces, and local storage require appropriate protection.
Protecting the device but ignoring APIs
A secure embedded device connected to an insecure API is still part of an insecure product.
Using shared credentials
Shared fleet credentials increase the blast radius if one credential becomes compromised.
Shipping without an update strategy
A product without a safe update mechanism can become permanently vulnerable.
Ignoring end of life
Stopping updates without informing customers can leave active installations exposed.
NIST's revised guidance specifically expands attention to maintenance, support, product lifespan, and end-of-life considerations.
Performance, Cost, and Security Considerations
IoT security always involves engineering trade-offs.
A small battery-powered sensor does not have the same processing capacity as an industrial gateway.
Strong security can affect:
- CPU utilization
- Memory
- Flash storage
- Battery consumption
- Network bandwidth
- Manufacturing cost
- Cloud infrastructure cost
That does not mean constrained devices should be insecure.
It means cybersecurity should be considered while selecting the MCU, communication architecture, memory, secure element, gateway architecture, and cloud services.
For example, adding secure key storage after hardware selection may require redesigning the PCB.
Planning it before hardware freeze may require only a small component change.
That difference illustrates why NIST's lifecycle-oriented approach matters commercially as well as technically.
Real-World Example: An Industrial IoT Monitoring Product
Imagine a manufacturer building wireless vibration sensors for industrial motors.
The original architecture
Each sensor:
- Measures vibration and temperature
- Sends data through a gateway
- Publishes telemetry to the cloud
- Displays equipment health in a dashboard
Functionally, everything works.
But the cybersecurity review discovers several weaknesses.
Devices share credentials.
Firmware cannot be remotely upgraded.
The gateway exposes unnecessary services.
Cloud permissions are broader than necessary.
There is no centralized security event logging.
The manufacturer has no documented vulnerability reporting process.
Applying the NIST approach
The team first maps the entire product.
Sensors → Gateway → Network → Cloud API → Database → Analytics → Dashboard
Then it performs threat modeling.
The manufacturer introduces:
- Unique device identities
- Certificate-based authentication
- Signed firmware
- Secure firmware updates
- Restricted gateway interfaces
- Least-privilege cloud permissions
- Centralized logs
- Vulnerability reporting procedures
- Defined security support periods
- An end-of-life communication process
The result is not simply a "more secure sensor."
It is a connected product that is easier to operate, investigate, update, and support throughout its deployed life.
NIST IR 8259 Rev. 1 vs. the Original Approach
The easiest way to understand the evolution is through four shifts.
From device to product
Security now needs to account for devices, gateways, applications, cloud services, and supporting components.
From development to lifecycle
Manufacturers need to consider what happens after deployment, including vulnerabilities, support, updates, and retirement.
From generic security to customer risk
Cybersecurity capabilities should reflect how customers actually deploy and depend on the product.
From features to ongoing capability
Encryption or secure boot alone does not make a product sustainably secure.
Manufacturers also need processes for vulnerability management, communication, updates, and long-term support.
Frequently Asked Questions
What is NIST IR 8259 Rev. 1?
NIST IR 8259 Rev. 1 is NIST's updated foundational cybersecurity guidance for IoT product manufacturers. The final publication was issued in April 2026 and supersedes NIST IR 8259 from 2020.
What changed in NIST's IoT cybersecurity guidance?
One major change is the broader focus on the complete IoT product rather than only the individual device. The revision also gives increased attention to risk assessment, threat modeling, post-market support, maintenance, and end-of-life considerations.
Does NIST require every IoT manufacturer to implement the same controls?
No. The guidance follows a risk-based approach. NIST's core baselines are intended as starting points that can be adapted to products, customers, markets, and risk environments.
What cybersecurity capabilities should IoT devices support?
NIST IR 8259A provides a core baseline of device cybersecurity capabilities. These cover areas such as device identification, configuration, data protection, interface access control, software updates, cybersecurity state awareness, and device security.
Is secure firmware enough?
No. Modern IoT products commonly depend on companion applications, gateways, cloud services, and other components. Customers expect security across the product rather than only inside the embedded device.
Should manufacturers perform threat modeling?
The revised guidance places greater emphasis on cybersecurity risk assessment and threat modeling during product development. NIST also references established resources that manufacturers can use when identifying threats.
What should happen after the IoT product ships?
Manufacturers should continue addressing cybersecurity through vulnerability remediation, product support, customer communication, software updates, incident response, and eventually product retirement.
Does NIST address IoT end of life?
Yes. The revised lifecycle perspective explicitly includes support expectations, product lifespan, software updates, and retirement considerations.
Where should a manufacturer start?
Start by mapping the entire connected product and its lifecycle.
Identify:
Devices → Firmware → Interfaces → Gateways → Applications → APIs → Cloud → Data → Operations → Support
Then determine customer needs, threats, cybersecurity requirements, technical controls, support responsibilities, and end-of-life plans.
IoT cybersecurity can no longer stop at the device. Manufacturers need to secure the entire connected product, from firmware and cloud services to updates, support, and end of life.

Conclusion
NIST IR 8259 Rev. 1 reinforces a shift that IoT manufacturers can no longer ignore: cybersecurity is a product lifecycle responsibility, not simply a device feature.
The practical change is to widen the security boundary. Manufacturers should look beyond firmware and hardware to the complete connected product, including gateways, APIs, cloud platforms, mobile apps, device management, update infrastructure, and operational support.
That also means moving security decisions earlier. Device identity, authentication, secure updates, threat modeling, vulnerability management, logging, customer communication, and end-of-life planning should be considered while the product architecture is still being designed.
For manufacturers, the objective is not to add every possible security control. It is to build a connected product whose risks are understood, whose security capabilities match its use case, and whose vulnerabilities can be managed throughout its operational life.
NIST's updated guidance provides a useful framework for making that shift.


